Picture a company that passes its yearly audit with flying colors. The checklist is complete, the policies are in place, and everyone feels safe. Three months later, an attacker gets in through a forgotten test server that nobody thought to look at. The audit never touched it.
What VAPT and a security assessment really are
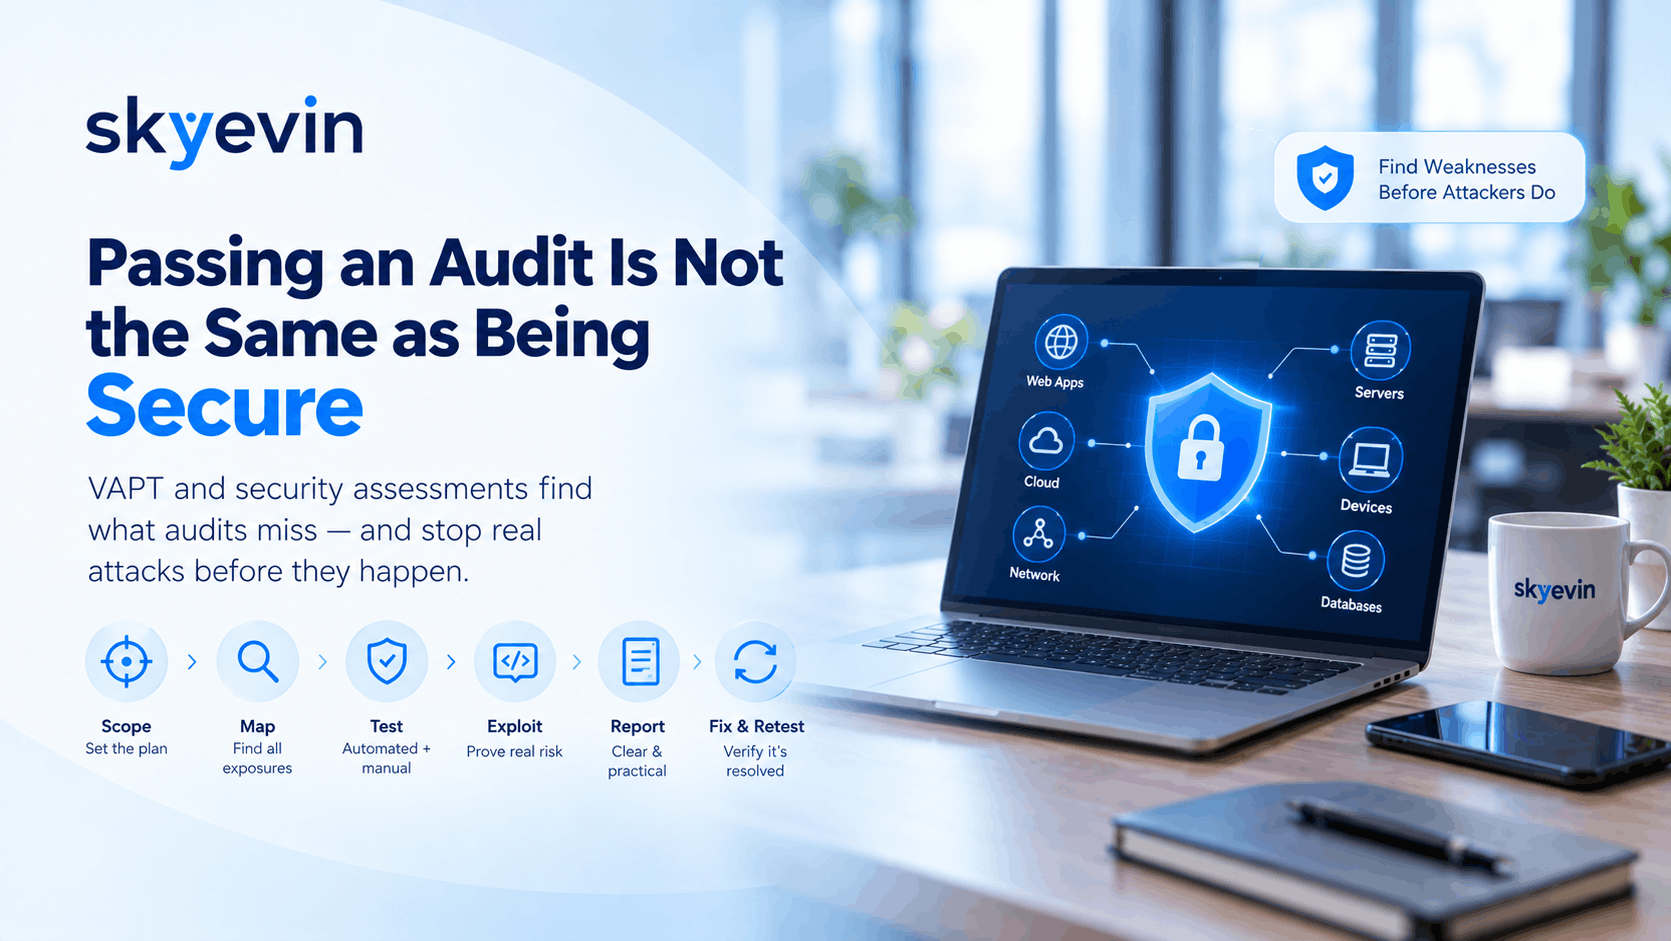
A security assessment is a broad review of your systems, settings, and processes. It shows where you are weak and how mature your defenses are. VAPT, short for Vulnerability Assessment and Penetration Testing, goes a step further. The assessment finds the weaknesses, and the penetration test then tries to use them, the way a real attacker would.
A simple way to think about it: a scan tells you which doors are unlocked, but a real test tells you whether someone can walk in and reach the safe.
Why you need it
Your systems change every week. New code, new cloud settings, and new integrations all create new gaps. Attackers only need to find one, while you need to close all of them. Customers and partners also ask more and more for proof that you take security seriously. And finding a weakness yourself costs far less than learning about it from a breach.
How we perform it
Scoping. We agree on what will be tested, how, and when, so there are no surprises.
Mapping. We discover everything that is exposed, including the systems your team may have forgotten.
Testing. Automated checks cover a lot of ground quickly. Manual testing then finds the issues that automation misses.
Careful exploitation. We prove which weaknesses truly matter and how small ones can be chained together into something serious, while keeping your live systems safe.
Reporting. You receive clear findings, ranked by real risk, each with a practical fix.
Fixing and retesting. We support your team while it fixes the issues, then test again to confirm the problems are gone.
What makes our approach different
We write reports that people can actually read. Every finding is explained in plain language, without a 200 page dump that nobody opens.
We give honest risk ratings. We do not inflate minor issues to look impressive or use scare tactics to win your attention.
We think like an attacker but act like a partner. That means we look for the creative paths a real intruder would take, and we protect your business while doing it.
Most importantly, our work does not end when the report is delivered. A finding that never gets fixed helps nobody, so we stay with you until the risk is actually reduced.
The bottom line
Security is not a certificate you earn once. It is something you keep testing, because your systems and the threats against them keep changing. A good VAPT gives you an honest picture of where you stand and a clear path to getting stronger.
Ready to see your systems the way an attacker does? Talk to our team about a security assessment tailored to your business.